Passing PECB ISO-IEC-27001-Lead-Auditor Exam Using 2026 Practice Tests [Q84-Q106]

Rate this post

Passing PECB ISO-IEC-27001-Lead-Auditor Exam Using 2026 Practice Tests

ISO-IEC-27001-Lead-Auditor Study Guide Brilliant ISO-IEC-27001-Lead-Auditor Exam Dumps PDF

PECB ISO-IEC-27001-Lead-Auditor Exam Syllabus Topics:

Section Weight Objectives
ISMS Audit Based on ISO 19011 and ISO/IEC 17021-1 25% – Auditing leadership commitment
– Continual improvement processes
– Auditing control selection and implementation (Annex A)
– Auditing the context of the organization
– Auditing risk assessment and treatment processes
– Auditing organizational structure and roles
– Measuring, monitoring, and reporting ISMS performance
Information Security Management Systems (ISMS) and the ISO/IEC 27001 Standard 15% – Regulatory and legal considerations in information security
– Fundamental principles and concepts of information security
– Overview of ISO/IEC 27001 and its relationship with ISO/IEC 27002
Audit Principles and Audit Process 20% – Audit sampling methodology
– Audit types and stages ( initiation, planning, execution, reporting)
– Risk-based audit approach
– Audit evidence collection techniques
– Audit scope and objectives
Certification and Accreditation Framework 15% – ISO/IEC 17021-1 requirements for certification bodies
– Audit report preparation and documentation
– Surveillance and re-certification audits
– Principles of certification bodies
– Certification decision process
Audit Lifecycle and Competencies of the Lead Auditor 25% – Audit follow-up and corrective action verification
– Leading an audit team
– Conflict resolution during audits
– Audit communication strategies
– Managing audit relationships with audited parties


NEW QUESTION 84
The scope of an organization certified against ISO/IEC 27001 states that they provide editing and web hosting services. However, due to some changes in the organization, the technical support related to the web hosting services has been outsourced. Should a change in the scope be initiated in this case?


NEW QUESTION 85
You are carrying out your first third-party ISMS surveillance audit as an Audit Team Leader. You are presently in the auditee’s data centre with another member of your audit team.
You are currently in a large room that is subdivided into several smaller rooms, each of which has a numeric combination lock and swipe card reader on the door. You notice two external contractors using a swipe card and combination number provided by the centre’s reception desk to gain access to a client’s suite to carry out authorised electrical repairs.
You go to reception and ask to see the door access record for the client’s suite. This indicates only one card was swiped. You ask the receptionist and they reply, “yes it’s a common problem. We ask everyone to swipe their cards but with contractors especially, one tends to swipe and the rest simply ‘tailgate’ their way in” but we know who they are from the reception sign-in.
Based on the scenario above which one of the following actions would you now take?


NEW QUESTION 86
The following are definitions of Information, except:


NEW QUESTION 87
You are an experienced ISMS audit team leader guiding an auditor in training. You decide to test her knowledge of follow-up audits by asking her a series of questions. Here are your questions and her answers.
Which four of your questions has she answered correctly?


NEW QUESTION 88
Select the correct sequence for the information security risk assessment process in an ISMS.
To complete the sequence click on the blank section you want to complete so that it is highlighted in red, and then click on the applicable text from the options below. Alternatively, you may drag and drop the options to the appropriate blank

NEW QUESTION 89
Scenario 9: UpNet, a networking company, has been certified against ISO/IEC 27001. It provides network security, virtualization, cloud computing, network hardware, network management software, and networking technologies.
The company’s recognition has increased drastically since gaining ISO/IEC 27001 certification. The certification confirmed the maturity of UpNefs operations and its compliance with a widely recognized and accepted standard.
But not everything ended after the certification. UpNet continually reviewed and enhanced its security controls and the overall effectiveness and efficiency of the ISMS by conducting internal audits. The top management was not willing to employ a full-time team of internal auditors, so they decided to outsource the internal audit function. This form of internal audits ensured independence, objectivity, and that they had an advisory role about the continual improvement of the ISMS.
Not long after the initial certification audit, the company created a new department specialized in data and storage products. They offered routers and switches optimized for data centers and software-based networking devices, such as network virtualization and network security appliances. This caused changes to the operations of the other departments already covered in the ISMS certification scope.
Therefore. UpNet initiated a risk assessment process and an internal audit. Following the internal audit result, the company confirmed the effectiveness and efficiency of the existing and new processes and controls.
The top management decided to include the new department in the certification scope since it complies with ISO/IEC 27001 requirements. UpNet announced that it is ISO/IEC 27001 certified and the certification scope encompasses the whole company.
One year after the initial certification audit, the certification body conducted another audit of UpNefs ISMS.
This audit aimed to determine the UpNefs ISMS fulfillment of specified ISO/IEC 27001 requirements and ensure that the ISMS is being continually improved. The audit team confirmed that the certified ISMS continues to fulfill the requirements of the standard. Nonetheless, the new department caused a significant impact on governing the management system. Moreover, the certification body was not informed about any changes. Thus, the UpNefs certification was suspended.
Based on the scenario above, answer the following question:
What type of audit is illustrated in the last paragraph of scenario 9?


NEW QUESTION 90
The following are definitions of Information, except:


NEW QUESTION 91
Which one of the following options is the definition of an interested party?


NEW QUESTION 92
Scenario 5: Data Grid Inc. is a well-known company that delivers security services across the entire information technology infrastructure. It provides cybersecurity software, including endpoint security, firewalls, and antivirus software. For two decades, Data Grid Inc. has helped various companies secure their networks through advanced products and services. Having achieved reputation in the information and network security field, Data Grid Inc. decided to obtain the ISO/IEC 27001 certification to better secure its internal and customer assets and gain competitive advantage.
Data Grid Inc. appointed the audit team, who agreed on the terms of the audit mandate. In addition, Data Grid Inc. defined the audit scope, specified the audit criteria, and proposed to close the audit within five days. The audit team rejected Data Grid Inc.’s proposal to conduct the audit within five days, since the company has a large number of employees and complex processes. Data Grid Inc. insisted that they have planned to complete the audit within five days, so both parties agreed upon conducting the audit within the defined duration. The audit team followed a risk-based auditing approach.
To gain an overview of the main business processes and controls, the audit team accessed process descriptions and organizational charts. They were unable to perform a deeper analysis of the IT risks and controls because their access to the IT infrastructure and applications was restricted. However, the audit team stated that the risk that a significant defect could occur to Data Grid Inc.’s ISMS was low since most of the company’s processes were automated. They therefore evaluated that the ISMS, as a whole, conforms to the standard requirements by asking the representatives of Data Grid Inc. the following questions:
*How are responsibilities for IT and IT controls defined and assigned?
*How does Data Grid Inc. assess whether the controls have achieved the desired results?
*What controls does Data Grid Inc. have in place to protect the operating environment and data from malicious software?
*Are firewall-related controls implemented?
Data Grid Inc.’s representatives provided sufficient and appropriate evidence to address all these questions.
The audit team leader drafted the audit conclusions and reported them to Data Grid Inc.’s top management.
Though Data Grid Inc. was recommended for certification by the auditors, misunderstandings were raised between Data Grid Inc. and the certification body in regards to audit objectives. Data Grid Inc. stated that even though the audit objectives included the identification of areas for potential improvement, the audit team did not provide such information.
Based on this scenario, answer the following question:
What would prevent the misunderstanding between the certification body and the Data Grid Inc.?
Refer to scenario 5.


NEW QUESTION 93
Question
Which statement regarding maintaining objectivity and impartiality of the internal audit is correct?


NEW QUESTION 94
Scenario 7: Webvue. headquartered in Japan, is a technology company specializing in the development, support, and maintenance of computer software. Webvue provides solutions across various technology fields and business sectors. Its flagship service is CloudWebvue, a comprehensive cloud computing platform offering storage, networking, and virtual computing services. Designed for both businesses and individual users. CloudWebvue is known for its flexibility, scalability, and reliability.
Webvue has decided to only include CloudWebvue in its ISO/IEC 27001 certification scope. Thus, the stage 1 and 2 audits were performed simultaneously Webvue takes pride in its strictness regarding asset confidentiality They protect the information stored in CloudWebvue by using appropriate cryptographic controls. Every piece of information of any classification level, whether for internal use. restricted, or confidential, is first encrypted with a unique corresponding hash and then stored in the cloud The audit team comprised five persons Keith. Sean. Layla, Sam. and Tin a. Keith, the most experienced auditor on the IT and information security auditing team, was the audit team leader. His responsibilities included planning the audit and managing the audit team. Sean and Layla were experienced in project planning, business analysis, and IT systems (hardware and application) Their tasks included audit planning according to Webvue’s internal systems and processes Sam and Tina, on the other hand, who had recently completed their education, were responsible for completing the day-to-day tasks while developing their audit skills While verifying conformity to control 8.24 Use of cryptography of ISO/IEC 27001 Annex A through interviews with the relevant staff, the audit team found out that the cryptographic keys have been initially generated based on random bit generator (RBG) and other best practices for the generation of the cryptographic keys. After checking Webvue’s cryptography policy, they concluded that the information obtained by the interviews was true. However, the cryptographic keys are still in use because the policy does not address the use and lifetime of cryptographic keys.
As later agreed upon between Webvue and the certification body, the audit team opted to conduct a virtual audit specifically focused on verifying conformity to control 8.11 Data Masking of ISO/IEC 27001 within Webvue, aligning with the certification scope and audit objectives. They examined the processes involved in protecting data within CloudWebvue. focusing on how the company adhered to its policies and regulatory standards. As part of this process. Keith, the audit team leader, took screenshot copies of relevant documents and cryptographic key management procedures to document and analyze the effectiveness of Webvue’s practices.
Webvue uses generated test data for testing purposes. However, as determined by both the interview with the manager of the QA Department and the procedures used by this department, sometimes live system data are used. In such scenarios, large amounts of data are generated while producing more accurate results. The test data is protected and controlled, as verified by the simulation of the encryption process performed by Webvue’s personnel during the audit While interviewing the manager of the QA Department, Keith observed that employees in the Security Training Department were not following proper procedures, even though this department fell outside the audit scope. Despite the exclusion in the audit scope, the non conformity in the Security Training Department has potential implications for the processes within the audit scope, specifically impacting data security and cryptographic practices in CloudWebvue. Therefore, Keith incorporated this finding into the audit report and accordingly informed the auditee.
Based on the scenario above, answer the following question:
To verify conformity to the protection of test data control, Webvue’s personnel simulated the encryption process. Is this acceptable?


NEW QUESTION 95
EquiBank is undergoing an external audit of its financial management system. The auditors evaluate the logic of transactions processed by EquiBank’s financial software. To ensure accuracy, they use simulations to validate operations, calculations, and controls programmed in the software applications. What type of Computer-Assisted Audit Technique (CAAT) is used?


NEW QUESTION 96
You are an experienced ISMS internal auditor.
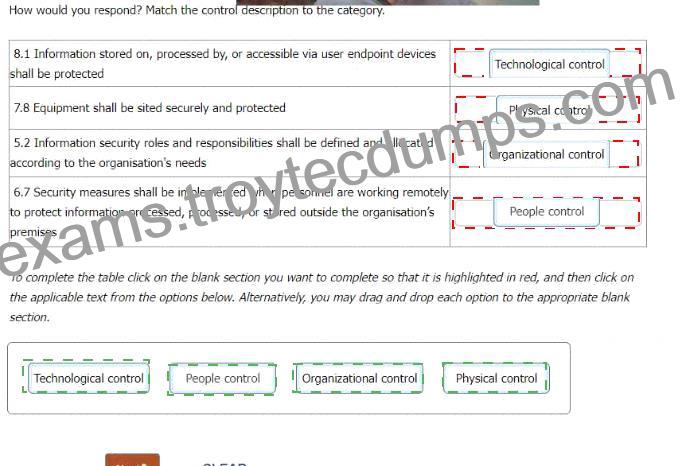
You have just completed a scheduled information security audit of your organisation when the IT Manager approaches you and asks for your assistance in the revision of the company’s Statement of Applicability.
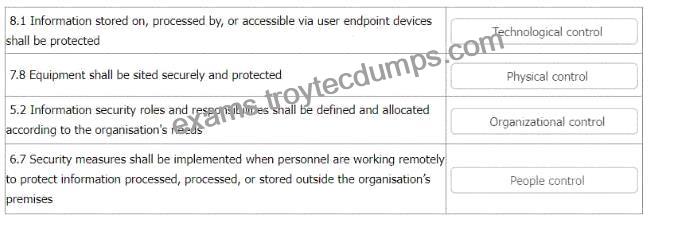
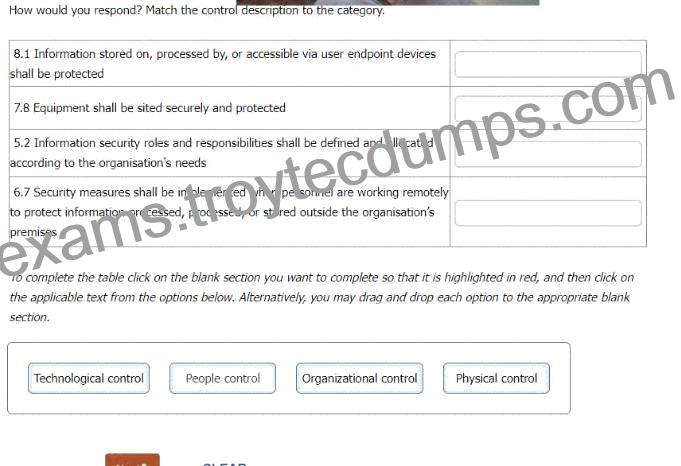
The IT Manager is attempting to update the ISO/IEC 27001:2013 based Statement of Applicability to a Statement aligned to the 4 control themes present in ISO/IEC 27001:2022 (Organizational controls, People Controls, Physical Controls, Technical Controls).
The IT Manager is happy with their reassignment of controls, with the following exceptions. He asks you which of the four control categories each of the following should appear under.
NEW QUESTION 97
You are an experienced ISMS audit team leader providing guidance to an auditor in training.
The auditor in training appears to be confused about the interpretation of competence in ISO 27001:2022 and is seeking clarification from you that his understanding is correct. He sets out a series of mini scenarios and asks you which of these you would attribute to a lack of competence. Select four correct options.


NEW QUESTION 98
You are an experienced ISMS audit team leader, talking to an Auditor in training who has been assigned to your audit team. You want to ensure that they understand the importance of the Check stage of the Plan-Do-Check-Act cycle in respect of the operation of the information security management system.
You do this by asking him to select the words that best complete the sentence:
To complete the sentence with the best word(s), click on the blank section you want to complete so that it is highlighted in red, and then click on the applicable text from the options below. Alternatively, you may drag and drop the option to the appropriate blank section.

NEW QUESTION 99
The audit lifecycle describes the ISO 19011 process for conducting an individual audit. Drag and drop the steps of the audit lifecycle into the correct sequence.

NEW QUESTION 100
You are carrying out your first third-party ISMS surveillance audit as an Audit Team Leader. You are presently in the auditee’s data centre with another member of your audit team.
Your colleague seems unsure as to the difference between an information security event and an information security incident. You attempt to explain the difference by providing examples.
Which three of the following scenarios can be defined as information security incidents?


NEW QUESTION 101
Which of the following is an information security management system standard published by the International Organization for Standardization?


NEW QUESTION 102
Scenario 2:
Clinic, founded in the 1990s, is a medical device company that specializes in treatments for heart-related conditions and complex surgical interventions. Based in Europe, it serves both patients and healthcare professionals. Clinic collects patient data to tailor treatments, monitor outcomes, and improve device functionality. To enhance data security and build trust, Clinic is implementing an information security management system (ISMS) based on ISO/IEC 27001. This initiative demonstrates Clinic’s commitment to securely managing sensitive patient information and proprietary technologies.
Clinic established the scope of its ISMS by solely considering internal issues, interfaces, dependencies between internal and outsourced activities, and the expectations of interested parties. This scope was carefully documented and made accessible. In defining its ISMS, Clinic chose to focus specifically on key processes within critical departments such as Research and Development, Patient Data Management, and Customer Support.
Despite initial challenges, Clinic remained committed to its ISMS implementation, tailoring security controls to its unique needs. The project team excluded certain Annex A controls from ISO/IEC 27001 while incorporating additional sector-specific controls to enhance security. The team evaluated the applicability of these controls against internal and external factors, culminating in the development of a comprehensive Statement of Applicability (SoA) detailing the rationale behind control selection and implementation.
As preparations for certification progressed, Brian, appointed as the team leader, adopted a self-directed risk assessment methodology to identify and evaluate the company’s strategic issues and security practices. This proactive approach ensured that Clinic’s risk assessment aligned with its objectives and mission.
According to Scenario 2, was the scope of Clinic’s ISMS determined correctly?


NEW QUESTION 103
Select the words that best complete the sentence below to describe audit resources:

NEW QUESTION 104
Select the words that best complete the sentence:

NEW QUESTION 105
As the ISMS audit team leader, you are conducting a second-party audit of an international logistics organisation on behalf of an online retailer. During the audit, one of your team members reports a nonconformity relating to control 5.18 (Access rights) of Annex A of ISO/IEC 27001:2022. The control was justified in the Statement of Applicability. She found evidence that removing the server access protocols of 20 people who left in the last 3 months took up to 1 week whereas the policy required removing access within 24 hours of their departure.
Select the three most appropriate actions taken by the auditee to deal with this situation.


NEW QUESTION 106
Select two options that describe an advantage of using a checklist.
* Using the same checklist for every audit without review


Free ISO-IEC-27001-Lead-Auditor Test Questions Real Practice Test Questions: https://www.troytecdumps.com/ISO-IEC-27001-Lead-Auditor-troytec-exam-dumps.html

Related Links: www.stes.tyc.edu.tw myportal.utt.edu.tt myportal.utt.edu.tt myportal.utt.edu.tt myportal.utt.edu.tt myportal.utt.edu.tt

troytecdumps

Learn More →

Leave a Reply

Your email address will not be published. Required fields are marked *

Enter the text from the image below